Full Stack
WorkMesh
Permission-aware company visibility
- Status
- Complete
- Year
- 2026
- Live application
- Runs locally with Docker Compose. Not publicly deployed.
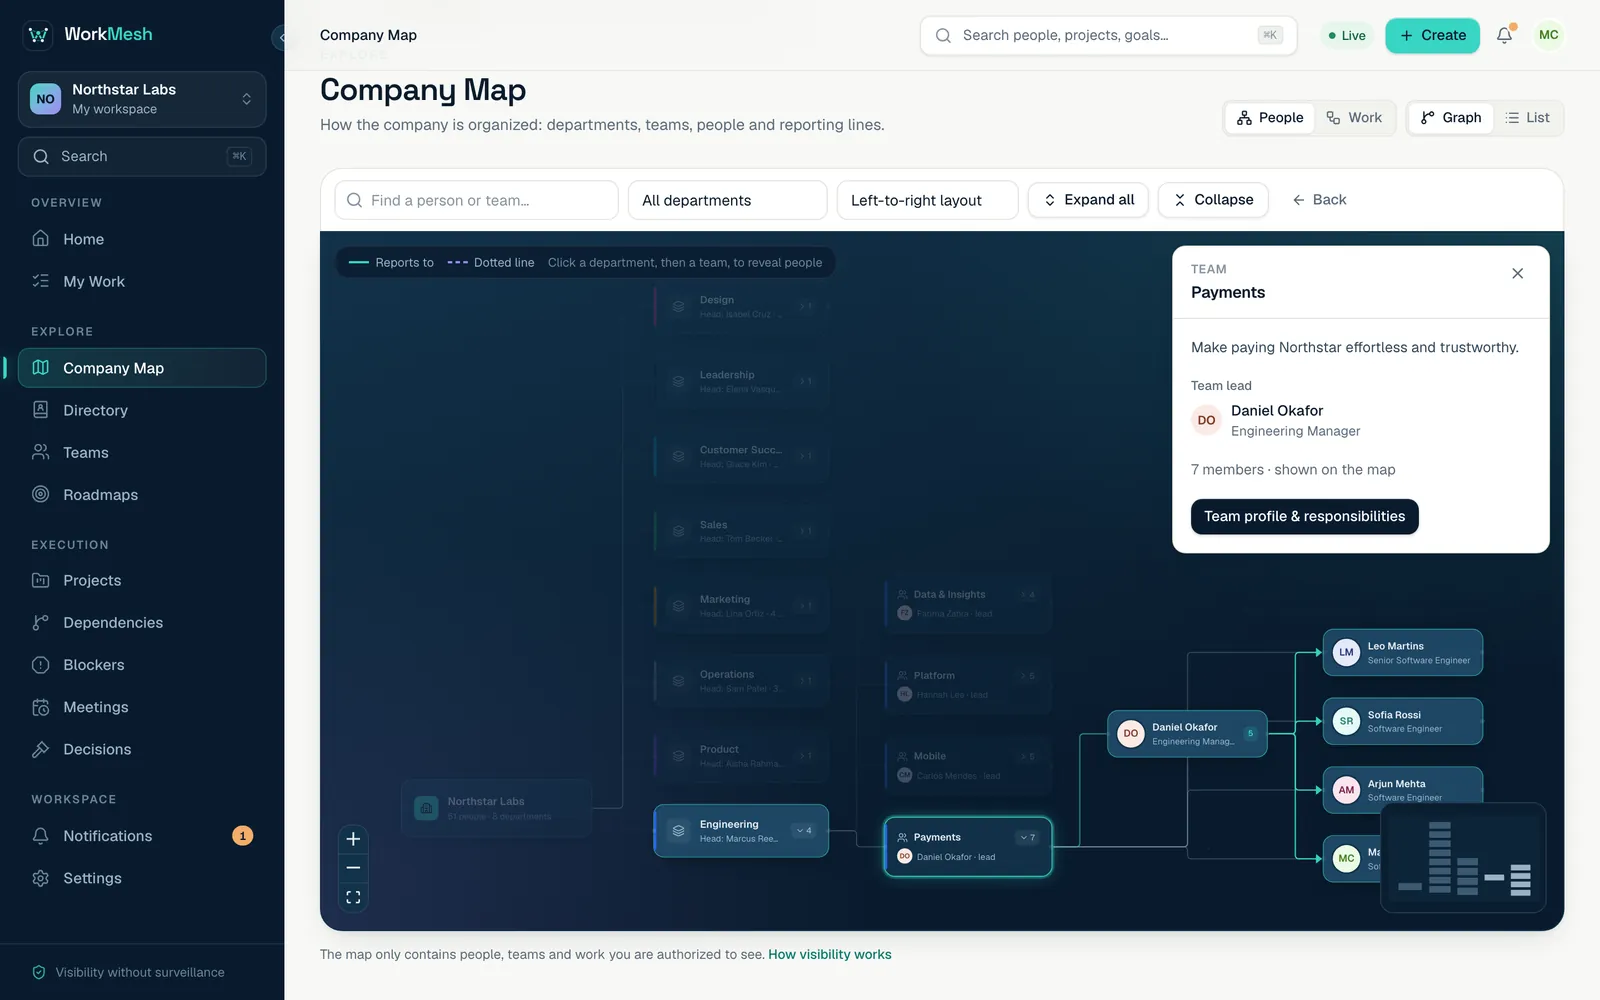
- p50, employee dashboard (300 requests, concurrency 10)
- 80 ms
- p50, employee dashboard (300 requests, concurrency 10)
- errors across the latency benchmark
- 0
- errors across the latency benchmark
- tenant tables under row-level security
- 35
- tenant tables under row-level security
01 Problem
In a small company, managers often don't know what everyone is working on and employees know the work of only a handful of colleagues. WorkMesh connects company → departments → teams → people with goals → initiatives → projects → milestones → work items, with permission-aware visibility and no surveillance.
02 Product overview
A modular NestJS monolith on PostgreSQL with row-level security powers an interactive Company Map, five role-based workspaces, roadmaps, a blocker state machine, a dependency graph with impact analysis and deterministic meeting briefs. Notifications flow through a transactional outbox, BullMQ and Socket.IO, re-authorizing every recipient before delivery.
Implemented
- Interactive Company Map (React Flow + ELK) with People and Work modes
- Five role workspaces: Employee, Manager, Project lead, Leadership, Admin
- Blocker state machine, roadmaps (timeline, board, list) and a dependency DAG with cycle prevention
- Deterministic meeting briefs with Markdown and print export
- Full-text search with authorization applied in SQL
- Admin permission inspector
Planned, not yet built
- Read-only calendar integration
- Per-field visibility policies
- SSO / SCIM
- Slack and Teams digests
- Historical health trends
03 System architecture
04 Core technologies
Backend
- NestJS 11
- Prisma 6
- PostgreSQL 16 (RLS, FTS)
- Redis 7
- BullMQ
- Socket.IO
- Zod
- Argon2id
Frontend
- Next.js 16
- React 19
- React Flow + ELK.js
- TanStack Query & Table
- Zustand
- Recharts
Quality
- Vitest
- Jest + Supertest
- Playwright
- gitleaks
- Docker
05 Engineering challenges
Authorization everywhere
Visibility rules apply to search, graphs, notifications and dashboards alike, so one pure policy engine is shared across the API and workers.
Realtime without leaks
Realtime events carry only IDs; clients fetch data through the same authorized API, and each recipient is re-authorized before delivery.
Defense in depth
35 tenant tables run with FORCE row-level security beneath the application-level checks.
06 Technical decisions
- 01Modular monolith over microservices
- 02Pure shared policy engine instead of an external authorization service
- 03Opaque sessions instead of JWTs
- 04Deterministic meeting briefs; no LLM
07 Verified test results
- Core (Vitest)
- 91
- API integration
- 54
- Web
- 16
- Playwright
- 9
Latest GitHub Actions run on main: passing. Counts as reported in the repository's README and testing docs.
Explore the results interactively in the Lab08 Screenshots
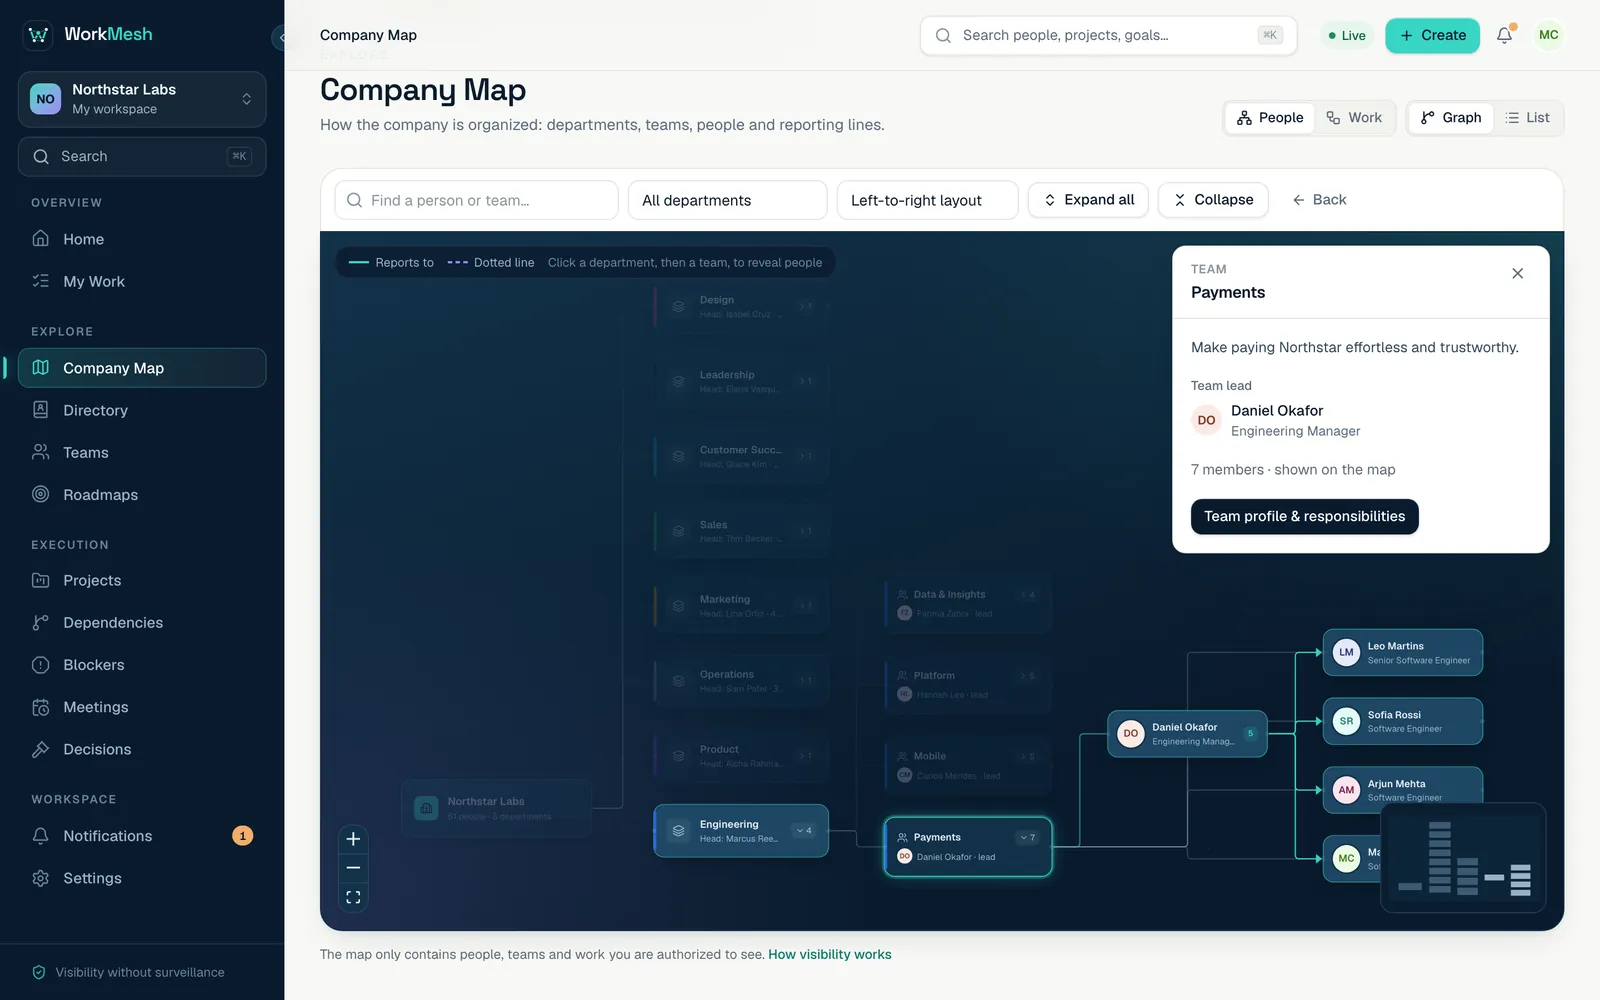
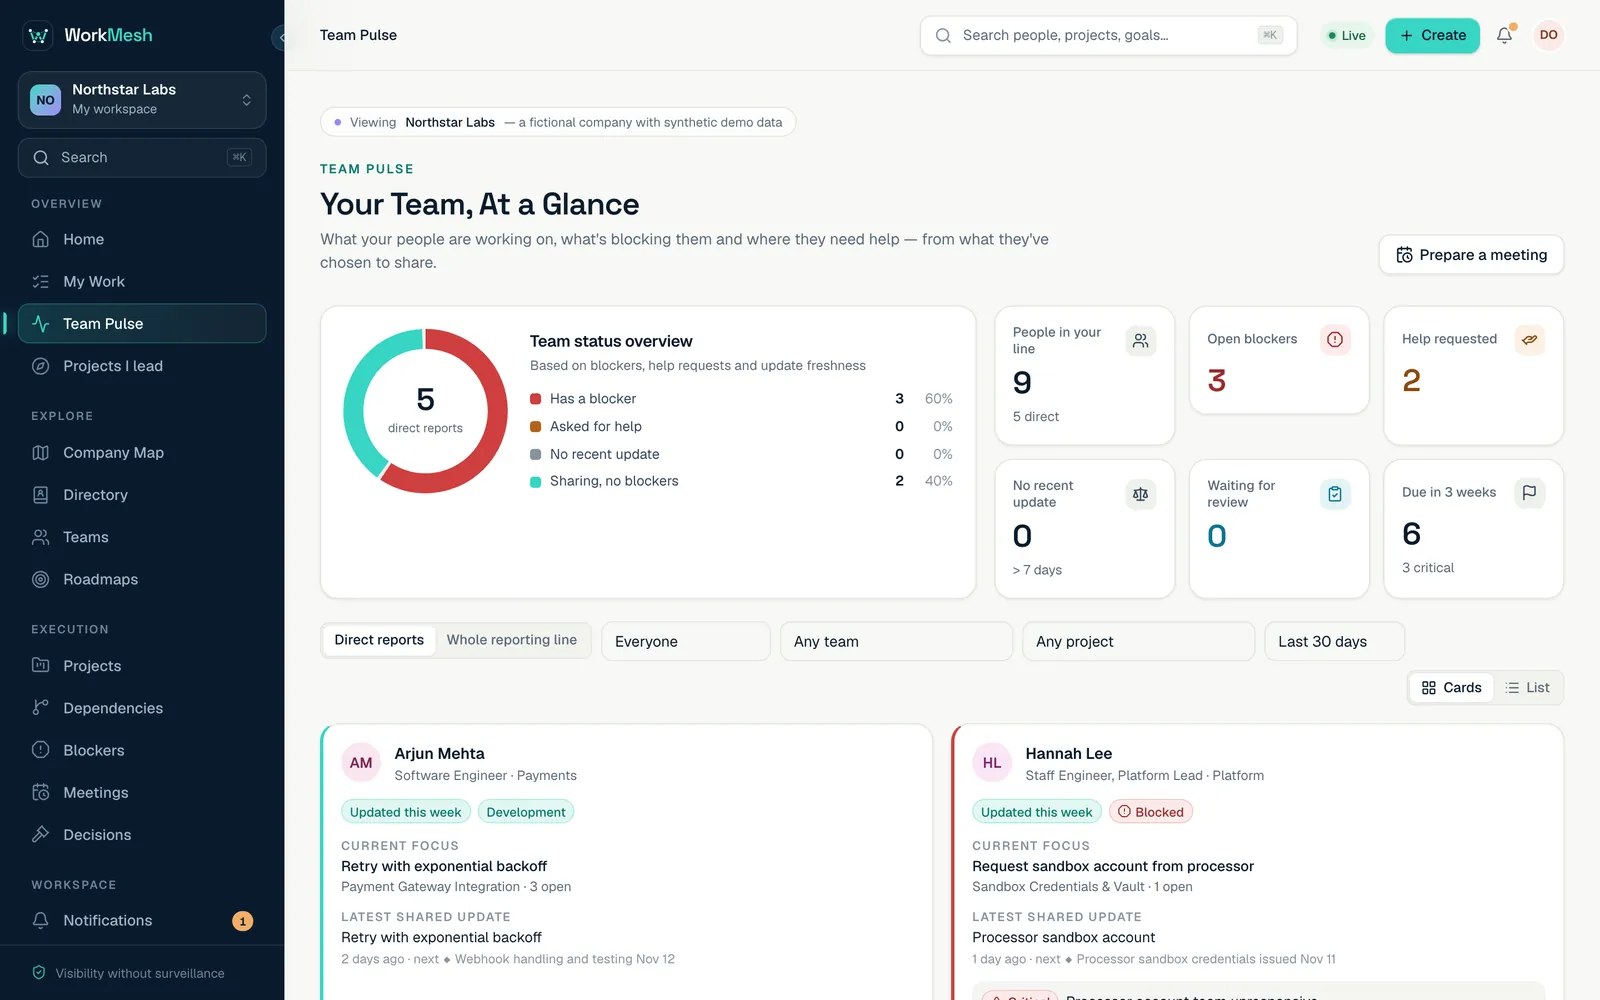
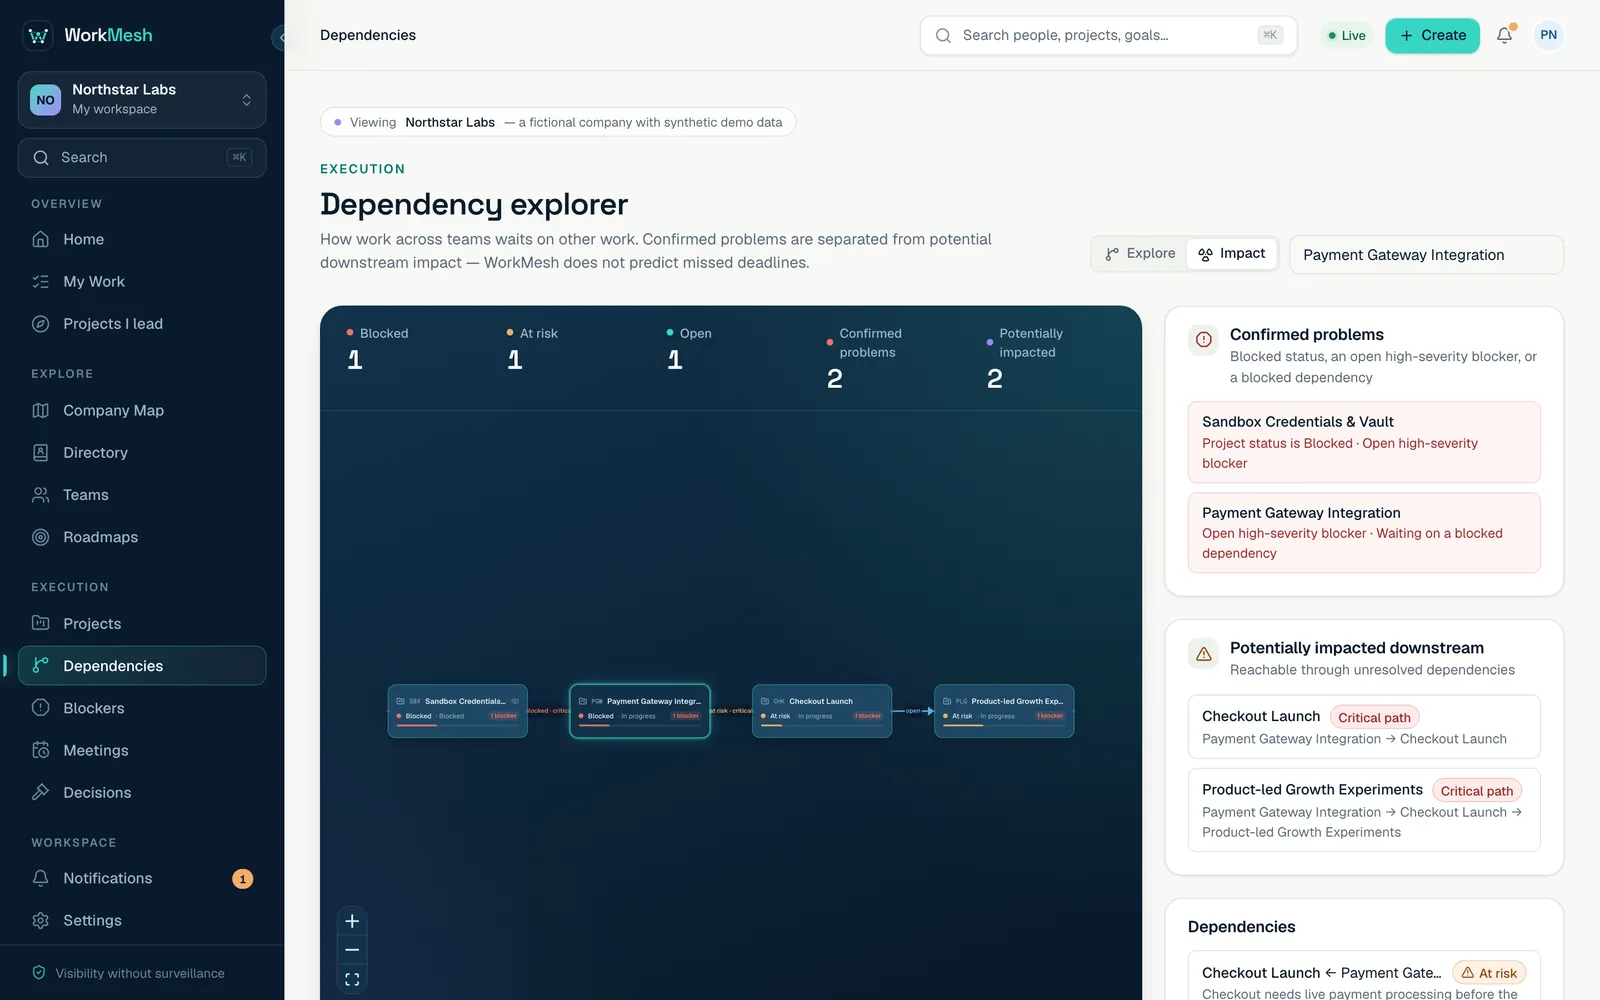
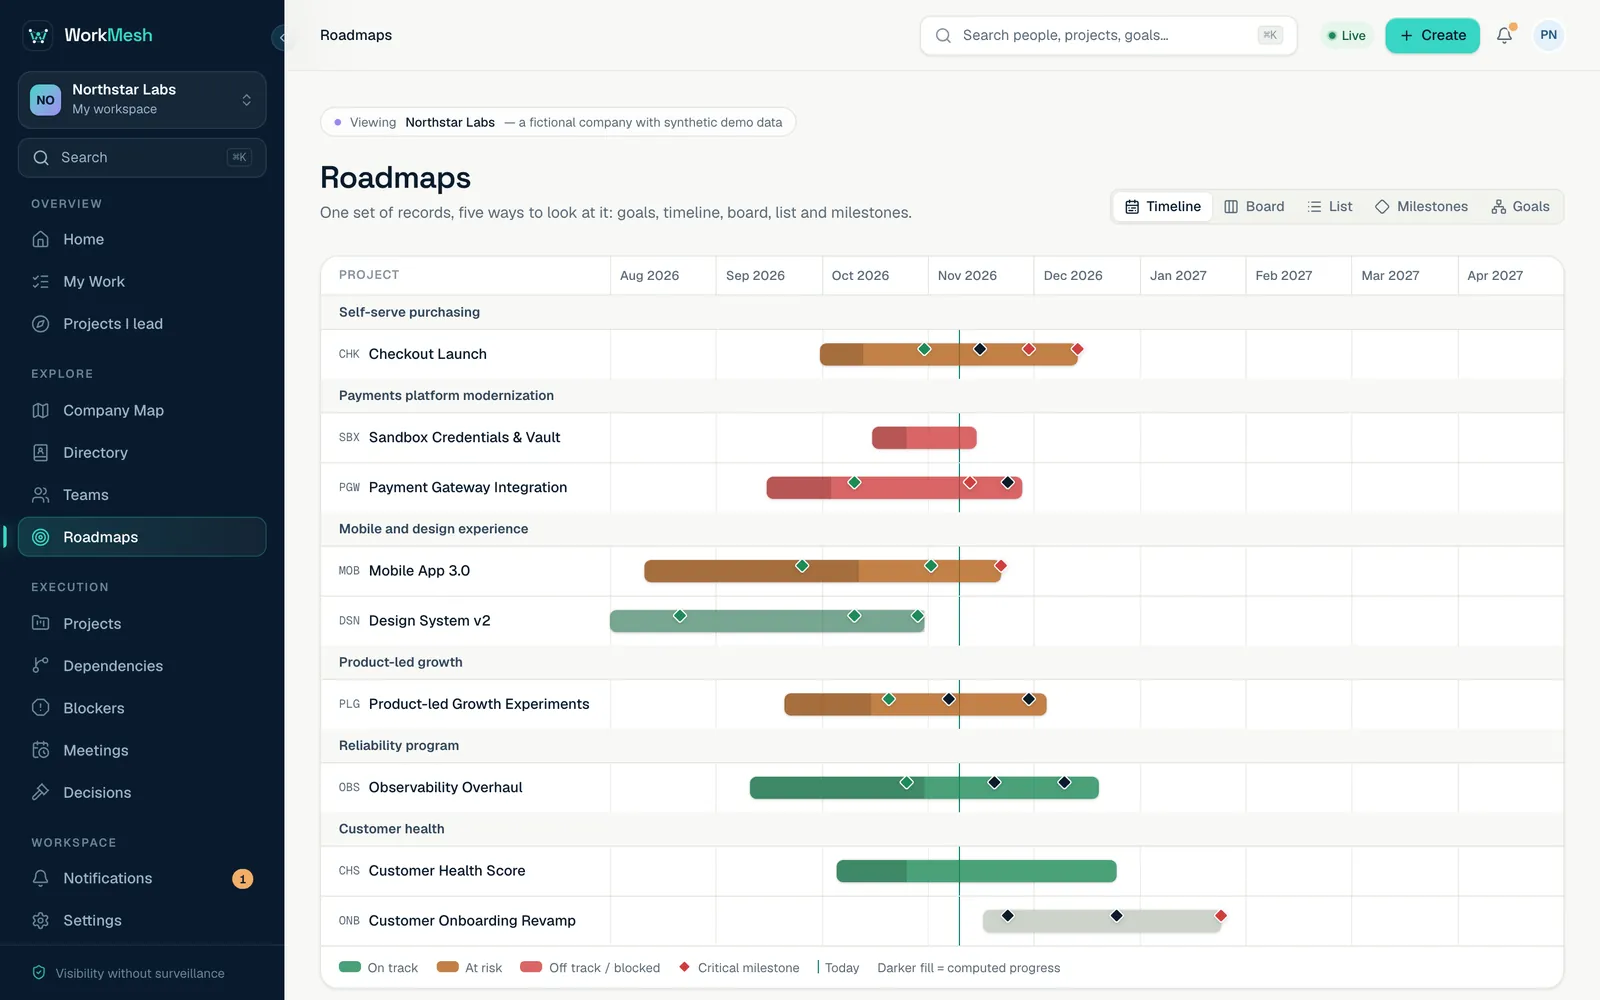
Screenshots captured from the running application and published in the repository's docs.
09 Links
No public deployment. Runs locally with Docker Compose. Not publicly deployed.